Trust, in one durable definition, is a willingness to be vulnerable, so is there a pain-free way to do it? Ask an Ethicist columnist Vera Cherepanova concludes there isn’t, and draws the line that matters: trust can deepen when a leader admits an honest limit, but the trust lost to an integrity breach can only be prevented, not repaired after the fact.
For the penultimate column of 2026 (in December we will have our traditional ethical barometer, summarizing what we talked about during the year), I want to examine a question I got from Jennifer Gaskin, editorial director of Corporate Compliance Insights. Earlier this year, a reader asked whether saying “I do not know” when a director is out of her depth on AI or another cutting-edge technology is part of good fiduciary conduct. I argued that it was and that boards should find pain-free ways to make such admissions possible. Jennifer came back to me on this with an excellent follow up: Are there really pain-free ways of being vulnerable? I was meaning to dig deeper into this fascinating topic when the right moment comes, and it feels like it’s here.
This question leads us directly to the concept of trust, because trust, at least according to one popular definition, is a willingness to be vulnerable to other people’s actions and intentions.
I must mention upfront that it always strikes me how trust, despite being so foundational and the most widely discussed topic in the social sciences, with over 120 definitions compiled across five decades of research, still remains elusive to define. But some folks got close.
Hernan Diaz, in his excellent novel “Trust” describes trust as “both a moral quality and a financial arrangement—as though virtue and money were synonymous.”
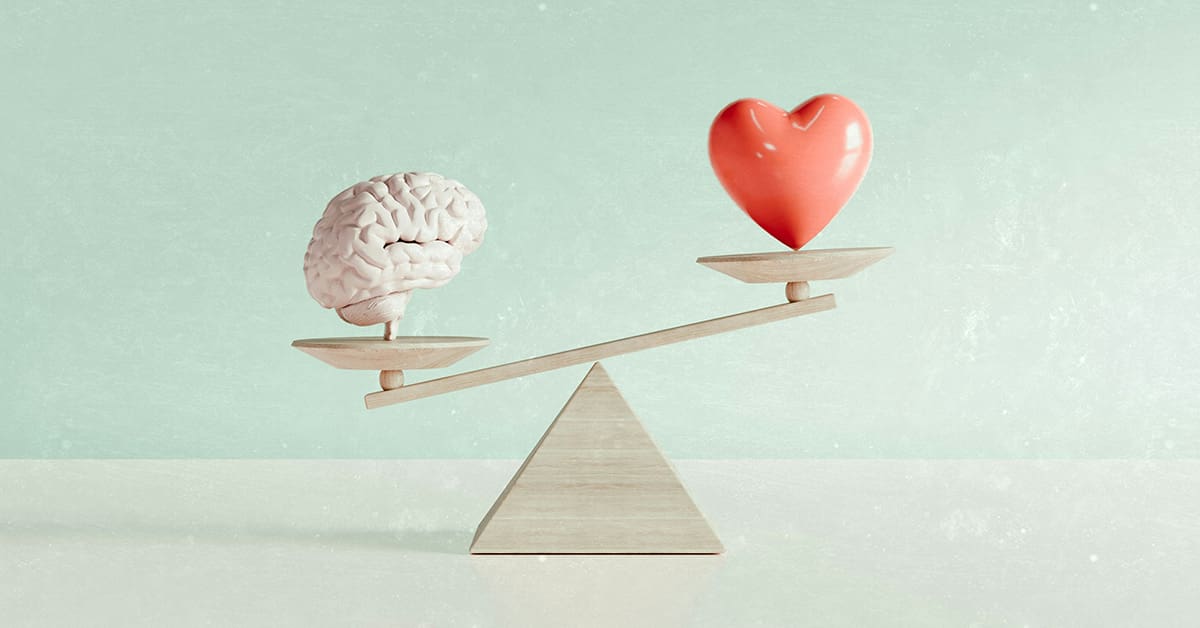
Indeed, trust seems to be a fusion of rational judgment and emotional connection. The decision to trust has both cognitive and affective components. Before trusting in someone, we want to know that they are competent and reliable. But these cognitive elements are insufficient on their own. We also want to know that they are honest and benevolent toward us in orientation. We trust, that is, from both the head and the heart.
Following from these dimensions of trustworthiness, one way to break it down is into four key tests of trust:
- Is it competent: does this person or tool work properly in this context?
- Is it reliable: can we count on this person or tool to work when we need to?
- Is it honest: are the functioning and the intent transparent?
- Is it benevolent: is it designed and deployed to serve our best interests?
It is the mix of the four that makes trust so challenging to build — and maintain.
Research on trust distinguishes between two kinds of trust breaches. A competence breach involves a failure of someone in the organization being unable to do their job, or unable to do it properly. An integrity breach involves a moral or ethical violation by the person or organization and has something to do with the character — or at least we perceive it as if it has. The thinking is that if they did this once, they may do it again.
A key difference between competence- and integrity-based breaches is the perception of intentionality. Integrity violations are viewed as a betrayal of the relationship and pose a greater challenge as they are much more likely to imperil an organization’s recovery, affective components at work.
So when a director admits, “I do not know this yet,” there might be a small cost to the competence component of trust: everyone on the board just has been reminded of the limits of her knowledge. But that is not a competence breach as such. I’d rather argue that pretending to know and failing to understand something you need to understand, and doing nothing about it, would be. Recognizing the limit and taking steps to close the knowledge gap can instead reinforce honesty, credibility and integrity.
Highly technological areas like AI or quantum computing should, at least in theory, make this even easier because no reasonable person can instantly follow every bit of their fast development. Here, “I don’t know” should be more acceptable. However, we are all familiar with how hype can get in the way and create the opposite pressure, with all directors feeling obliged to sound as though they understand everything. So, the important thing to watch out for is letting hype crowd out reason.
There is a world of difference between making oneself vulnerable by admitting a limitation and becoming vulnerable because conduct has called one’s integrity into question.
The ongoing Nvidia CEO scandal gives us a contemporary illustration of how questions about the integrity of a corporate leader can create wider organizational vulnerability, affecting not only the individual but also the board, succession, stakeholders and the company’s reputation. It is a developing story, with many facts still unknown or unconfirmed, but the controversy is obviously being processed as a breach of integrity.
So, where does this land us? By definition, vulnerability implies accepting some possibility of discomfort or harm. It also means accepting the possibility that what we reveal may change how others see us. Therefore, completely pain-free ways to be vulnerable probably do not exist, and that’s part of that inexplicable magic of trust.
However, there are ways to make the right kinds of vulnerability less painful, and intellectual humility firmly is one of them.
At the same time, competence-related and integrity-related vulnerability are strikingly different. When vulnerability comes from an integrity failure, the only way to make it less painful is not cultural normalization or better trust repair (looking at you, PR colleagues) but preventing the ethical violation in the first place.
When in Rome? The Risks of Ethics & Compliance Bending to Local Norms
The question of whether ethics are universal or local is as old as philosophy, and the AI race has made it urgent again
Read moreDetailsReaders respond
The previous column tackled the perennial tension between global ethical standards and local norms. The question came from a compliance officer wondering what global compliance means in an increasingly fragmented world and whether compliance standards now need to bend more to local custom.
In my response, I noted: “Companies generally have global zero-tolerance policies toward fraud or sexual harassment. Such a prohibition is derived from idealism since the ban on these two types of conduct is universal throughout the company.
“On the other hand, the policy toward salespeople offering gifts to clients may vary based on geography. For instance, salespeople based in the US may be prohibited from offering cash gifts to potential clients, since this could be construed as bribery. Meanwhile, the same company’s sales team in parts of Asia may be permitted, based on appropriate guidelines and policies, to give small cash gifts when attending the weddings of customers or clients, because such cash gifts are an integral aspect of many Asian cultures. This variation in gift-giving policy is derived from relativism, since the policy is based on the ethical and moral principles of different cultures.
“Seng-ts’an, a Chinese Buddhist philosopher, wrote that “the struggle between ‘for’ and ‘against’ is the mind’s worst disease.” Put another way, in my loose interpretation, failure to see nuance is often not a sign of moral clarity but evidence of oversimplification and a lack of thought.
“What makes your question particularly worthwhile to ponder is that the old philosophical problem is suddenly of interest outside the E&C geeks’ bubble. Now we want machines to align with human values, although, as we’ve just seen, we have never agreed on what those universal values are, and for good reason.” Read the full column here.
“It’s about accountability. Why has the [Hugging Face] attack not resulted in legal action against the designers of a system that acted illegally? The answer is the tech industries have swerved this by anthropomorphizing the systems. ‘It’s the systems that did it, Your Honour.’” — JS

 Vera Cherepanova