Internal Audit

Gartner: Internal Audit Is at Risk of Being Overstretched in 2021
As Well As Reducing Budgets, The COVID-19 Pandemic Has Heightened Organizational Risks and the Need for Audit Oversight Stamford, CT (March 24, 2021) – A September 2020 study of 299 internal audit organizations showed that the function faced both declining budgets and a significantly expanded workload in 2020, according to Gartner, Inc. “For many heads of audit, it’s not clear where the extra capacity is going to come from,” said Margaret Moore Porter, Managing Vice President in the Gartner Audit...

AICPA: Implications of Blockchain in SOC for Service Organization Examinations
The American Institute of CPAs (AICPA) today issued a new whitepaper to help auditors providing SOC for Service Organization (SOC) reports on organizations that have incorporated blockchain into their service delivery systems. The paper examines the skills and competencies auditors need to perform such engagements, the unique features of blockchain, the risks associated with using blockchain, and how the use of blockchain by service organizations may affect their SOC examinations. Highlights include: An overview of blockchain, including a discussion of the different...

Protiviti & ISACA: IT Audit Perspectives 2021
Global consulting firm Protiviti recently released the findings from its latest study, “IT Audit Perspectives: Top Technology Risks in 2021,” which reveals that concerns around security, privacy, cloud and other advanced technologies are being further fueled by the pandemic-induced remote work environment and accelerated deployment of new technologies. The study, conducted in partnership with ISACA, surveyed over 7,400 IT audit leaders across a wide range of industries worldwide. The report identifies the top 10 IT Audit risks for 2021 and examines how digital leaders weigh...

Fintech Pressure on Internal Audit
Banks have long outsourced certain audits, but banking-fintech relationships are new ground. Brandi Reynolds discusses a persistent problem in bank internal audit departments and offers a path forward. Co-sourcing or outsourcing certain internal audits is nothing new to bank internal audit departments. In the 1980s, IT/MIS (management information systems) functions started growing in sophistication, and all but the largest banks outsourced their IT audits. In the early 2000s, Bank Secrecy Act functions also grew in sophistication and outgrew the capabilities...

4 Tips for Conducting Virtual Internal Audits
As COVID-19 rages on, companies continue to go digital. Riskonnect CEO Jim Wetekamp offers guidance on how to conduct successful audits in a remote work environment. As the COVID-19 pandemic magnifies existing threats and constantly creates new risks for organizations to assess, business leaders are seeking added assurance that appropriate oversight, capabilities and controls are in place – and they are looking to internal audit for help. With remote work and travel restrictions limiting mobility in many parts of the...

The Growing Need for Business Continuity Audits
COVID-19 has revealed the importance of having an effective business continuity plan. Protiviti’s Matthew Watson discusses the role internal audit should play in escalating and prioritizing business continuity audits given the realities and uncertainties in today’s business environment. With so many uncertainties as we head into 2021 – the wait for an effective COVID-19 vaccine, macroeconomic and geopolitical concerns, increased technology outages and cybersecurity risks to name a few – business continuity programs have taken on new urgency. Business leaders,...

4 Considerations When Auditing Revenue Recognition
Auditors need a complete understanding of the standard and how it affects their clients’ financial statements. AICPA’s Deana Thorps suggests four considerations auditors need to keep in mind when performing high-quality audits based on common challenges with accounting estimates. One of the most significant changes to U.S. GAAP is FASB’s revenue recognition standard, FASB ASC Topic 606, Revenue from Contracts with Customers. The standard requires an entity to apply a five-step approach, including estimating the revenue recognized for the accounting...

Accounting for Loss Contingencies – “Hindsight is 20/20”
Ron Kral offers an analysis of the SEC’s recent order against BorgWarner, charged for making material misstatements by failing to account for certain asbestos liabilities. “Hindsight is 20/20” can be a profound statement when it comes to loss contingencies, as it is easy to precisely define them once they are settled over time. The statement can also be interpreted as the company should have known something would happen, or the company made a bad decision in hindsight. In applying this...

Independence of the Compliance Function: A Critical Component of the Three Lines Model
Ellen McCarthy, Head of Compliance at Computershare, opines on the IIA’s recent updates to its three lines of defense model, positing that they fail to recognize the importance of the independence of the compliance function. The Institute of Internal Auditors (IIA) last month issued a new three lines model, updating its “Three Lines of Defense” model to set forth the IIA’s “latest understanding of governance and risk management.” Below, I have set out my personal view along that, while the...

Getting More From Internal Audit in the Digital Age
With digitization fueling innovation and change, two questions arise: Is internal audit adjusting quickly enough to innovate and embrace underlying technologies, and should executive management and the board care? Protiviti’s Jim DeLoach discusses. In a world of rapid change on almost every front, in which organizations must adapt and grow – or risk decline and ultimate demise – everybody faces the same reality: either raise the game to contribute sustainable value or be left at the station. These words could...
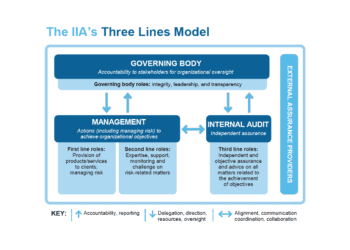
Does the New Three Lines Model Give Short Shrift to Compliance?
Compliance doesn't appear to figure prominently in the update to the Institute of Internal Auditors' 2013 Three Lines of Defense Model. Compliance consultant Nicole Di Schino takes a look here, providing original reporting for CCI as she shares analysis and opinions from compliance pros and IIA CEO Richard Chambers. All images courtesy of Institute of Internal Auditors; used with permission Recent updates to the Institute of Internal Auditors’ (IIA) three lines of defense model offer a refreshing take on corporate...
Preparing for Annual SOX Compliance Amid COVID-19
Protiviti’s Shari Katz and Gina Chaoanw outline steps organizations can take in pursuit of annual SOX compliance and as they use third parties to navigate the challenges arising from COVID-19. More and more companies are outsourcing key business processes to third-party providers to attain cost savings and to focus on core business activities. As a result, when management needs to assess its internal controls over financial reporting (ICFR), many of these outsourced activities fall into scope for Sarbanes-Oxley (SOX) compliance....